Our team

You are buying people, not a brochure.

Industrial security advice is only as good as the person giving it. Here is who leads the work, and what they are accountable for.

Leadership

Who leads the practice.

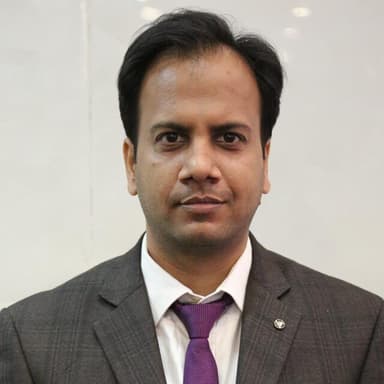
Rachana Singh

Co-Founder & Chief Executive Officer

LinkedIn

Rachana Singh is a Cybersecurity and OT/ICS leader with over 16 years of experience across cyber risk management, IT/OT security, ICS security, railway cybersecurity, DCS engineering and critical infrastructure protection. She is CEO of SVRA Tech Cyber LLP, delivering cybersecurity consulting, assurance, engineering and risk management.

Her sector experience spans railway, automotive, oil and gas, energy, power, manufacturing, chemical and critical infrastructure — combining technical depth in DCS, industrial automation and OT/ICS environments with security architecture, risk advisory, governance and programme management.

She has led multidisciplinary teams on complex projects, bridging engineering, operations, cybersecurity, safety and business risk, with global experience in strategic programme management, technical assurance, project controls and stakeholder management.

Leads on
Cyber risk managementRailway cybersecurityDCS & industrial automationCritical infrastructure protectionGovernance & programme delivery
Think tank

Industry mentors.

Senior practitioners who challenge our thinking and shape the direction of our community work — education, open research and the wider effort to close the OT security skills gap.

Each mentor holds a full-time role elsewhere and contributes to SVRA in a personal capacity. They hold no executive or fiduciary position in the firm, and their views are their own.

Rajeev Gupta

Rajeev Gupta

Risk, compliance & certification

A risk and compliance professional with more than 30 years of experience turning international standards into practical, business-aligned programmes across telecom, banking, professional services, media, PSUs, BPOs and automotive. He contributed to the Cloud Security Alliance Cloud Controls Matrix as a working group committee member, has guided multiple organisations to ISO 27001:2022 certification, and is currently supporting a Tier 1 UK telecom provider on Telecom Security Act compliance. He also built a CISA exam-preparation question bank used by candidates worldwide.

ISO 27001:2022CSA Cloud Controls MatrixBusiness continuity & DRBusiness impact analysisUK Telecom Security ActLead audit & implementation
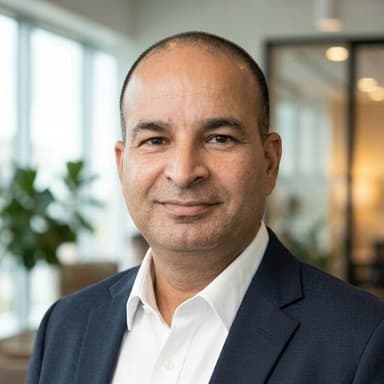
Rajiv Goyal

Rajiv Goyal

Enterprise technology & architecture

Over 20 years of experience with banks and financial institutions including Wells Fargo, American Express and CITCO Hedge Fund Services, across India, the US and Canada. He has architected and built business-critical systems on microservices, APIs, web applications and mobile platforms, and has led teams delivering highly available, scalable enterprise solutions.

Enterprise architectureMicroservices & APIsFinancial services technology
Varun Verma

Varun Verma

Digital commerce & platforms

A senior eCommerce specialist with more than 20 years in software development and services for multi-brand global retailers in apparel, luxury and fashion, across B2C and B2B. His work spans pre-sales, consulting, solution design and delivery on Salesforce Commerce Cloud (Demandware) and IBM WebSphere Commerce, with working knowledge of SAP Hybris and Adobe AEM, in retail, BFSI and education.

Salesforce Commerce CloudIBM WebSphere CommerceJava / J2EERetail & BFSI
Dushyant Gautam

Dushyant Gautam

Project management

A project manager with over 28 years of experience, an engineering foundation and a specialised focus on project delivery, holding a Bachelor's degree in Engineering, a PG Diploma in Project Management and PMP certification. He works on large-scale projects across a range of sectors, covering project lifecycles, resource allocation, risk management and stakeholder communication, and leads cross-functional teams in high-pressure environments.

LinkedIn
Vishal Sharma

Vishal Sharma

Project controls & risk advisory

A project controls and risk advisory leader with nearly two decades on global capital projects. He has led greenfield, brownfield and asset migration programmes across oil and gas, energy, manufacturing, chemicals and automotive, covering project controls, scheduling, cost engineering, procurement and operational risk.

Enterprise & operational riskProject controls governancePlanning & schedulingCost engineeringQMS audits

Join the think tank

Senior practitioners in OT security, compliance or critical infrastructure who want to mentor the next generation of engineers — we would like to hear from you.

Get in touch
How we work

What we can tell you.

We do not publish a wall of client logos. Assessment findings are confidential, and a logo tells you nothing about the work.

We assess against the standards we help write

ISA/IEC 62443 for industrial systems, CLC/TS 50701 for rail, ISO/SAE 21434 and ISO 24089 for automotive, ISO/IEC 42001 for AI management systems.

Sectors we work in

Power generation, transmission and distribution, rail, automotive manufacturing and supply, process industries, telecom infrastructure and smart metering.

We publish our method, not our clients

Engagements are confidential. What we put in the public domain is analysis and approach — through the newsletter, whitepapers and training material.

The wider problem

There are not enough OT security engineers.

Every asset owner we speak to has the same constraint: the standards are clear enough, but the people who can apply them to a live plant are scarce. IT security professionals know the frameworks and not the process; control engineers know the process and not the threat model.

That gap is why we train as well as consult. The consulting work keeps the training honest, and the training is how the capability outlasts any single engagement.

Build the capability in-house

We run cohorts for asset-owner and vendor teams covering the IEC 62443 series, sector frameworks and assessment practice — taught from engagements rather than slideware.

Want to know who would actually run your engagement?

Tell us the sector and the constraint. We'll tell you who would lead it and whether we are the right people for it.